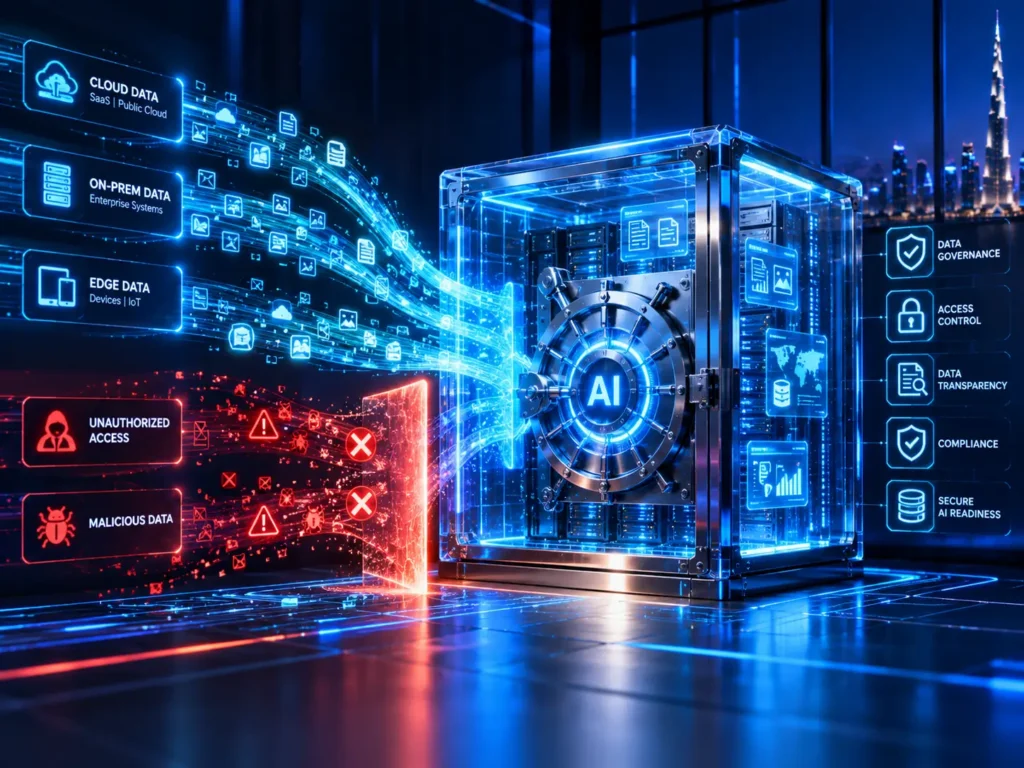
An effective AI governance framework defines who is accountable for AI systems, which rules they must follow, and how those rules are enforced and evidenced while the systems are actually running. The last part is where many frameworks fall short: policies and checklists approve a model at launch, but risk appears in production, request by request.
Runtime governance closes that gap by turning written policy into technical controls that act on every prompt, tool call and output, and by producing the evidence that proves they did.
Why checklist governance breaks down
Traditional model risk management assumed relatively static models that were validated once and monitored periodically. Generative AI and agents break those assumptions.
- Behaviour depends on prompts, retrieved context and tools, all of which change continuously.
- Foundation models are updated by providers, sometimes with limited notice.
- Users can push a system into situations no pre-launch review anticipated.
- Agents take actions, so a governance lapse becomes an operational incident, not just a poor answer.
A launch checklist is still useful. It simply cannot be the whole framework. Governance has to continue at the speed the system runs.
The four layers of an AI governance framework
A practical framework has four layers. The first two are familiar to most risk teams; the last two are where runtime governance lives.
| Layer | Purpose | Examples |
|---|---|---|
| Principles and accountability | Set intent and ownership | AI principles, risk appetite, named owners per system, governance board |
| Policies and standards | Translate intent into rules | Data classification rules, approved model list, acceptable use, human oversight requirements |
| Runtime controls | Enforce rules on live traffic | Gateway policy checks, input and output filtering, tool permission enforcement, rate and spend limits |
| Evidence and assurance | Prove controls worked | Tamper-evident logs, evaluation results, incident records, periodic control testing |
Each policy in the second layer should map to at least one control in the third and one evidence source in the fourth. If a policy has no control, it is an aspiration. If a control produces no evidence, it cannot be audited.
Turning policies into runtime controls
The translation from policy to control is the heart of the work. A few examples show the pattern:
- Policy: confidential data must not be sent to external models. Control: the gateway classifies prompts and routes confidential requests only to private or in-region models.
- Policy: agents must not make payments above a set value without approval. Control: the payment tool enforces a threshold and holds requests for human sign-off.
- Policy: outputs must not reveal other customers’ personal data. Control: retrieval scoped to the requesting user’s permissions, plus output scanning.
- Policy: model changes require re-validation. Control: deployment pipelines block a new model or prompt version until evaluations pass.
Express these rules as versioned policy code where possible, so changes are reviewed, tested and reversible like any other software change. Enforcement points usually sit in a shared gateway or an AI control plane, rather than in each application.
Evidence: what auditors and regulators will ask for
Runtime governance only counts if you can demonstrate it. Plan the evidence trail from the start.
- Request-level logs linking each interaction to an identity, model version, policy version and outcome, with sensitive content handled under your retention and privacy rules.
- Policy decision records showing which rule allowed, blocked or modified a request.
- Evaluation history for every model and prompt version that reached production.
- Human oversight records capturing who approved what, and on what information.
- Incident and exception logs with root cause and remediation.
Logs can themselves become a data protection risk if they store prompts containing personal data. Apply the same classification and access controls to telemetry that you apply to source data; our article on LLM data leakage through logs and embeddings covers this in detail. Strong AI observability is the foundation that makes this evidence practical to collect.
Aligning the framework with UAE and international expectations
Organisations in the UAE operate against a backdrop that includes Federal Decree-Law No. 45 of 2021 on personal data protection, the separate data protection regimes of DIFC and ADGM, sector regulators, and the ambitions of the UAE National Strategy for Artificial Intelligence 2031. Many also serve customers in other jurisdictions with their own AI and data rules.
Rather than building a separate framework for each regime, design one control set and map it to multiple obligations. Runtime controls such as data residency routing, access scoping and audit logging tend to satisfy overlapping requirements. Confirm specific obligations with your legal and compliance teams, as this article is not legal advice.
Getting started in the first 90 days
A realistic first phase does not attempt to govern everything at once:
- Inventory production AI systems and agents, with an accountable owner for each.
- Pick the three policies that carry the most risk and implement them as runtime controls.
- Route all model traffic through a single gateway that logs policy decisions.
- Agree a minimum evidence pack per system and test that it can be produced on request.
Expand from there, adding controls as new use cases and agents arrive, and review the framework itself whenever regulation or architecture changes.
Who runs the framework day to day
A framework needs an operating rhythm as well as documents. Many organisations appoint a small AI governance function that maintains the policy library, owns the control mapping and chairs a regular review with security, data, legal and business representatives. Platform engineering owns the enforcement points, while system owners remain accountable for their own AI applications and agents. Keeping these roles distinct stops governance from becoming either a paper exercise or a bottleneck, and gives auditors a clear line of accountability from policy to evidence.
Take runtime governance further at Enterprise Private AI UAE 2027
Enterprise Private AI UAE 2027 runs on 17–18 March 2027 in Dubai. On Day 2, the Governance Session AI Governance at Runtime: Moving Beyond Policies and Checklists focuses directly on the shift described here, while the CXO Panel Private AI for Regulated Industries: Architecture Under Real Constraints explores how regulated organisations apply governance in practice. Expect a curated room of CISOs, CIOs, heads of AI and enterprise architects, with speakers from organisations including KPMG, Accenture, Infosys and Microsoft. See the programme, view passes, or submit an abstract if you have a governance story to share.
Frequently asked questions
What is an AI governance framework?
An AI governance framework defines who is accountable for AI systems, which rules they must follow, and how compliance is enforced and evidenced. Effective frameworks cover principles, policies, runtime controls and assurance.
What is runtime AI governance?
Runtime AI governance enforces policy on live AI traffic, checking each prompt, tool call and output as it happens. It complements launch reviews by catching risks that only appear in production.
What should an AI governance framework include?
It should include named owners, policies and standards, technical controls that enforce them, and evidence such as logs, evaluations and approval records. Each policy should map to a control and an evidence source.
Does an AI governance framework need to reflect UAE law?
Organisations operating in the UAE should map their framework to applicable rules, including Federal Decree-Law No. 45 of 2021 and, where relevant, DIFC or ADGM data protection regimes. Confirm specific obligations with legal and compliance advisers.