Confidential AI is the use of confidential computing, meaning hardware-based trusted execution environments (TEEs), to protect data, prompts and model weights while an AI workload is actually running. It closes the gap left by conventional encryption, which protects data at rest and in transit but not while it sits decrypted in memory during inference or training.
For enterprises weighing whether sensitive workloads can run on shared infrastructure, confidential AI offers a way to reduce how much you must trust the cloud operator, the host administrator or anyone else with access to the underlying machines. This guide explains how it works, where it fits and what it does not solve.
The data-in-use gap in enterprise AI
Most organisations already encrypt data at rest and in transit. The weak point is the moment of processing. To run inference, a model’s weights and the user’s prompt are loaded into memory in plain form, where a privileged administrator, compromised hypervisor or malicious insider could, in principle, read them.
For many AI workloads this matters a great deal:
- Prompts may contain customer records, financial positions, health information or legal strategy.
- Retrieved context in RAG systems often includes the organisation’s most sensitive documents.
- Fine-tuned model weights can represent valuable intellectual property.
- Regulators and customers increasingly ask not just where data is stored, but who could access it during processing.
How confidential AI works
Confidential AI combines several building blocks that together make the processing environment both isolated and verifiable.
Trusted execution environments
A TEE is a hardware-enforced region where code and data are isolated from the rest of the system, including the operating system and hypervisor. Memory is encrypted with keys held by the processor. CPU technologies such as Intel TDX and AMD SEV-SNP protect whole virtual machines, and some recent data-centre GPUs, such as NVIDIA’s Hopper generation, add a confidential computing mode so that accelerated inference can run inside the protected boundary.
Remote attestation
Isolation alone is not enough; you need proof. Attestation produces a cryptographically signed report describing the hardware, firmware and software running in the TEE. Before releasing anything sensitive, your systems verify that report against the configuration you expect.
Attestation-gated key release
The most powerful pattern ties decryption keys to attestation. A key management service only releases the keys for model weights or encrypted data once the environment has proven it is genuine and unmodified. If anything changes, the keys stay locked.
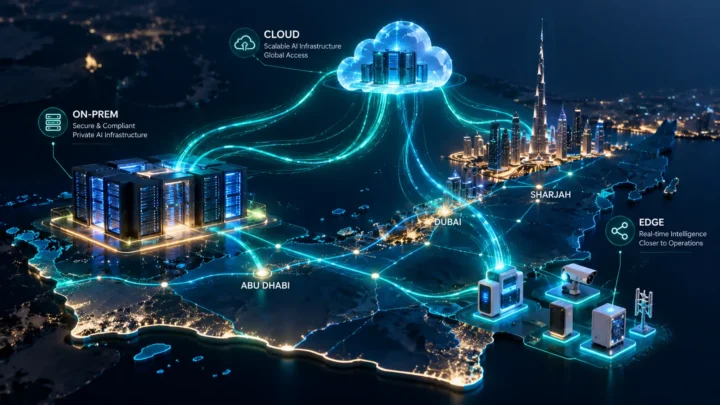
In practice, these pieces are usually consumed as a managed service: confidential virtual machines or confidential GPU instances from a cloud provider, combined with an attestation service and a key management system you control. On-prem deployments can use the same hardware features, which is useful when you want verifiable isolation between internal tenants or business units sharing one GPU cluster.
Enterprise use cases for confidential AI
Confidential AI is most valuable where sensitive data and shared or third-party infrastructure meet.
- Sensitive inference in the public cloud. Run models on cloud GPUs while limiting the provider’s ability to see prompts and outputs.
- Protecting model intellectual property. Deploy proprietary or fine-tuned models to a customer site or partner cloud without exposing the weights.
- Multi-party data collaboration. Let several organisations combine data for analysis or model training without any party seeing the others’ raw data.
- Sovereignty and regulated workloads. Add a technical assurance layer to location and contractual controls when handling regulated data.
- Edge deployments. Where hardware support exists, protect models and data on devices that sit outside physically secure facilities.
Confidential AI vs other privacy-enhancing approaches
Confidential computing is one of several techniques for protecting data in AI systems. Each has different trade-offs, and they are often combined.
| Approach | What it protects | Main trade-offs |
|---|---|---|
| Encryption at rest and in transit | Stored and transmitted data | Data is exposed in memory during processing |
| Confidential computing (TEEs) | Data and models in use, plus verifiable integrity | Hardware dependency, operational complexity, some performance overhead |
| On-prem or dedicated infrastructure | Physical and administrative control | Capital cost, capacity planning, insider risk remains |
| Masking and tokenisation | Specific sensitive fields | Can reduce model usefulness; context may still reveal information |
| Homomorphic encryption | Computation on encrypted data | Currently impractical for most large-model workloads |
| Differential privacy | Individuals within training data | Accuracy trade-offs; does not protect inference prompts |
The choice often feeds into a broader question of which parts of the stack to own and which to rent, explored in our article on the sovereign AI stack.
Limitations and design considerations
Confidential AI is a strong control, but it is not a cure-all. Plan for these realities:
- It does not fix application-layer risks. Prompt injection, over-privileged agents and leaky logs remain your responsibility. See our guide to LLM data leakage in logs and embeddings.
- You must verify attestation yourself. The value depends on checking reports against an expected configuration, not simply enabling a feature.
- Trust shifts rather than disappears. You still rely on the hardware vendor and the attestation chain.
- Performance and availability vary. Overhead depends on workload and hardware, and confidential GPU capacity may not be offered in every region.
- Data leaving the enclave is unprotected. Outputs written to logs, caches or downstream systems need their own controls.
Confidential computing can support data protection obligations, for example under UAE Federal Decree-Law No. 45 of 2021 or the DIFC and ADGM regimes, but it does not by itself make a workload compliant. Our article on private AI and UAE data law covers the wider picture; confirm specifics with your legal and compliance teams.
Getting started with confidential AI
A focused pilot is the best way to learn what confidential AI means for your workloads.
- Pick one high-value workload, such as inference on regulated customer data or a proprietary fine-tuned model.
- Confirm hardware and regional availability with your cloud or infrastructure provider.
- Design attestation-gated key release so data and weights only decrypt inside verified environments.
- Measure performance against your current deployment to understand real overhead.
- Close the gaps around the enclave, including logging, output handling and zero trust controls for users and agents.
See confidential AI in context at Enterprise Private AI UAE 2027
Confidential computing has its own spotlight at Enterprise Private AI UAE 2027 in Dubai on 17–18 March 2027. The Security Keynote Confidential AI: Protecting Data While Models Are Actually Running (Day 2, 11:30) explores how enterprises protect data in use, following the Architecture Deep Dive Data Control Beyond the Model (Day 2, 10:45).
Join CISOs, CTOs and architects in a curated room, with speakers from organisations including Microsoft, Capgemini and Accenture. View the agenda, choose your pass or explore partner deep-dive labs if you build confidential computing solutions.
Frequently asked questions
What is confidential AI?
Confidential AI is the use of confidential computing to protect data, prompts and model weights while an AI workload is running. Hardware-based trusted execution environments keep memory isolated and encrypted so that even the infrastructure operator cannot read it.
How does confidential AI differ from encryption?
Standard encryption protects data at rest and in transit, but data must normally be decrypted in memory to be processed. Confidential AI extends protection to data in use by processing it inside a hardware-isolated environment whose integrity can be verified through attestation.
Do GPUs support confidential computing?
Yes, some recent data-centre GPUs, such as NVIDIA's Hopper generation, offer a confidential computing mode that works alongside CPU trusted execution environments. Availability varies by cloud provider and region, so check with your provider before designing around it.
Where can I learn more about confidential AI in the UAE?
Enterprise Private AI UAE 2027 in Dubai on 17–18 March 2027 includes a Day 2 Security Keynote titled Confidential AI: Protecting Data While Models Are Actually Running, alongside sessions on data control and regulated industries.