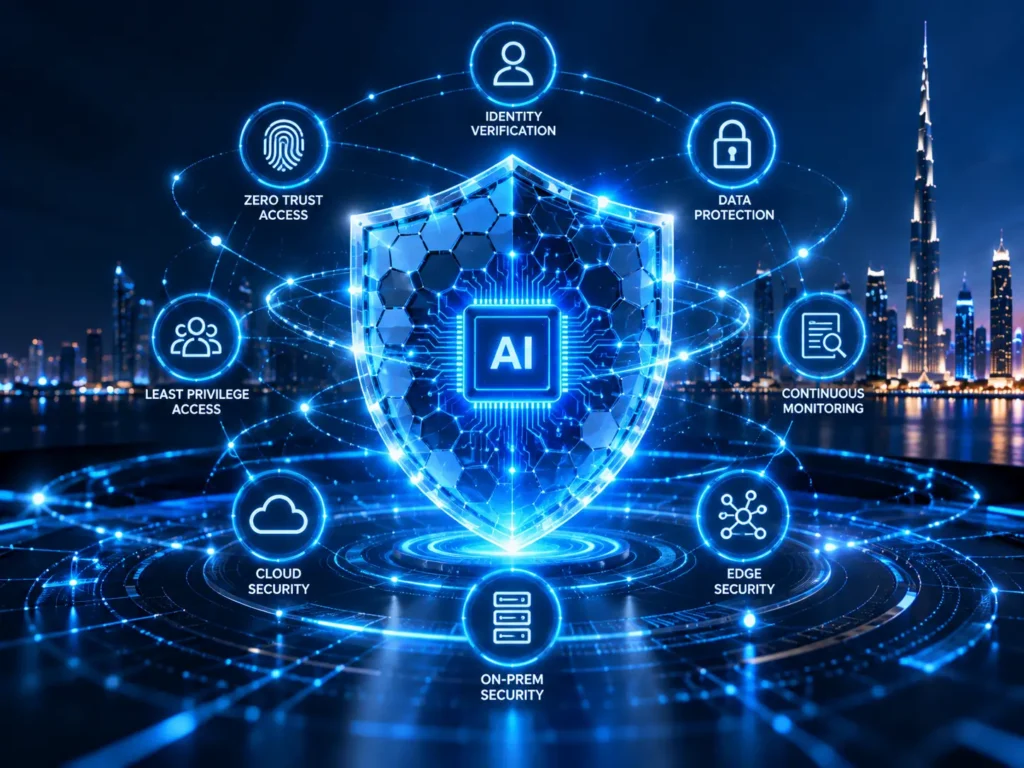
Zero trust AI security means applying never trust, always verify to every component of an AI system: users, applications, models, agents, data pipelines and the infrastructure they run on. Instead of assuming anything inside the network is safe, each request to a model, tool or dataset is authenticated, authorised and logged on its own merits.
That matters because enterprise AI breaks the old perimeter. A single assistant can call a hosted model, query a vector database, read from a document store and trigger an action in a business system, often across cloud, on-prem and edge environments. This guide sets out the principles, a control map and a phased way to roll zero trust out across your AI estate.
Why AI systems break perimeter security
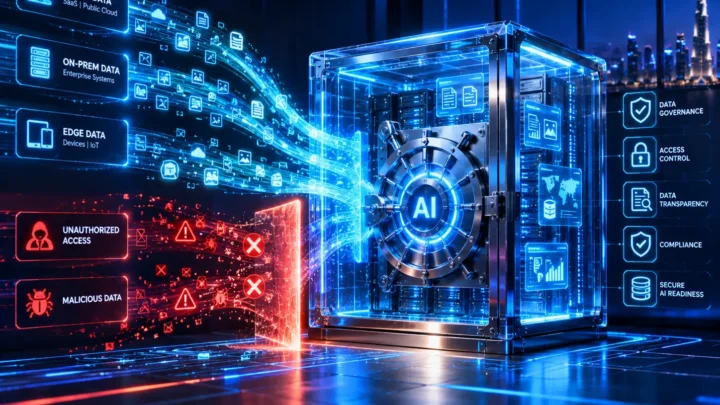
Traditional security models drew a line around the data centre and trusted what was inside. AI workloads ignore that line. Prompts arrive from employees, customers and partner systems; models may be self-hosted, rented as an API or both; and retrieval pipelines pull content from sources with very different sensitivity levels.
Three characteristics make AI especially awkward for perimeter thinking:
- Natural language is an attack surface. Instructions and data travel in the same channel, so malicious text hidden in a document or email can steer a model. This is why prompt injection sits at the top of the OWASP Top 10 for LLM Applications 2025 as LLM01.
- Models act on behalf of people. When an assistant or agent calls tools, it inherits permissions. If those permissions are broad, a single manipulated prompt can reach a long way.
- Data flows multiply. Prompts, completions, embeddings, logs and fine-tuning sets all carry fragments of sensitive information, and every copy needs protection.
Core principles of zero trust AI security
The zero trust principles most security teams already know translate well to AI, but each needs an AI-specific interpretation.
Verify explicitly
Every call to a model endpoint should carry a strong identity: the human user, the calling application and, for agents, the agent itself. Shared API keys embedded in code are the opposite of zero trust. Use short-lived tokens issued by your identity provider and bind them to a specific workload.
Least privilege, per request
Grant access to models, tools and data based on the task at hand, not the broadest role a user holds. A retrieval pipeline should only return documents the requesting user could already open. An agent drafting an email should not also hold permission to approve payments.
Assume breach
Design as if a prompt will eventually be manipulated or a model will eventually output something it should not. That means validating outputs before they reach downstream systems, segmenting environments and keeping enough telemetry to reconstruct exactly what happened.
A zero trust control map for the AI stack
It helps to break the AI stack into layers and assign controls to each. The table below is a starting map rather than a complete standard; adapt it to your own architecture and risk appetite.
| Layer | What to verify | Example controls |
|---|---|---|
| Users and applications | Who is asking, and from which device and app | SSO, MFA, device posture checks, per-application client credentials |
| AI gateway | Which model, which policy, which budget | Central routing, prompt and output filtering, rate limits, audit logging |
| Models | Provenance and integrity of weights | Signed artefacts, an approved model registry, isolated serving environments |
| Retrieval and data | Whether the user may see each source | Document-level access control, data classification, permission-filtered vector search |
| Agents and tools | Which actions are permitted | Scoped tool permissions, allow-lists, human approval for high-impact steps |
| Infrastructure | Where workloads run and who can reach them | Network segmentation, workload identity, encryption, confidential computing for sensitive inference |
Applying zero trust across cloud, on-prem and edge
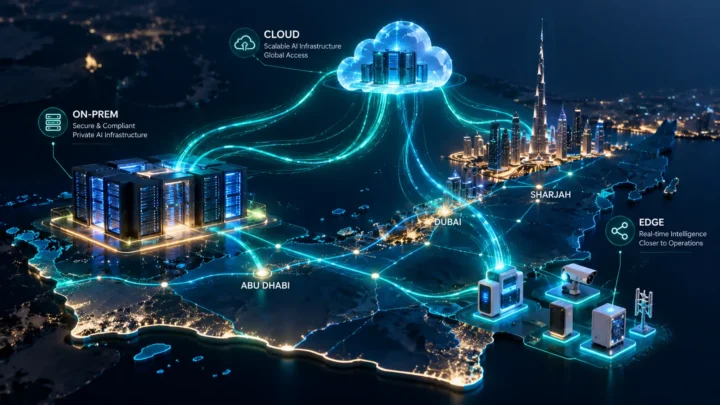
Most enterprises will not run AI in one place. Sensitive workloads may stay on-prem or in a sovereign cloud region, general productivity use may go to a hosted API, and latency-critical inference may move to the edge. Zero trust gives you one consistent security model across all three.
The AI gateway from the control map is what makes that consistency practical. Routing all model traffic through one controlled layer gives you a single place to enforce policy, inspect content and record activity, whether the model behind it is a public API, a self-hosted model served with an engine such as vLLM, or a small model running at the edge.
- Cloud: use private endpoints rather than public internet paths where providers support them, apply workload identity, and review the provider’s data retention and logging terms carefully.
- On-prem: do not assume the data centre is a safe zone. Segment GPU clusters, restrict administrative access and treat model weights as sensitive assets.
- Edge: devices are physically exposed, so rely on hardware-backed identity, encrypted storage, signed model updates and the ability to revoke a device quickly.
For organisations in the UAE, location and control decisions also intersect with data protection obligations under Federal Decree-Law No. 45 of 2021 and, for entities in DIFC or ADGM, their own regimes. Our guide to private AI in the UAE covers deployment options in that context; always confirm specifics with your legal and compliance teams.
A phased roadmap to zero trust for AI
Zero trust is a programme rather than a product. A phased approach keeps momentum without stalling AI delivery.
- Inventory. List every model, endpoint, agent, vector store and AI-enabled SaaS feature in use, including shadow usage by individual teams.
- Centralise access. Route model traffic through a gateway and replace static keys with identity-based, short-lived credentials.
- Enforce data boundaries. Apply classification and permission-aware retrieval so the model only sees what the user is entitled to see.
- Constrain agents. Scope tool permissions narrowly and add human approval for irreversible or high-value actions. Our guide to AI agent identity and access covers this in depth.
- Monitor and test. Log prompts, outputs and tool calls with appropriate redaction, run regular red-team exercises and feed the findings back into policy.
If you want a control-by-control mapping against the OWASP list, read Zero Trust for LLMs. For the wider programme view, see our enterprise AI security best practices.
Common zero trust mistakes in AI programmes
- Treating the model provider’s security as your security. Provider controls protect their platform, not your permissions model.
- Giving a retrieval system a service account that can read everything, which quietly bypasses document permissions.
- Logging full prompts and completions without redaction, creating a new store of sensitive data.
- Relying on system prompts to enforce rules. Instructions to a model are guidance, not access control.
- Securing the pilot but not the production rollout, where usage, integrations and risk grow quickly.
Each of these mistakes shares a root cause: trust granted implicitly because a component sits inside the architecture. Making that trust explicit, scoped and observable is the whole point of the zero trust approach.
Explore zero trust AI security at Enterprise Private AI UAE 2027
Zero trust for AI is a central thread on Day 2 of Enterprise Private AI UAE 2027, held in Dubai on 17–18 March 2027. The Technical Keynote Securing LLMs Across Hybrid Enterprise Environments (Day 2, 10:00) examines how to apply consistent controls across cloud, on-prem and edge, while the Deep-Dive Lab AI Identity: Who — or What — Should an Agent Be Allowed to Do? (Day 2, 14:45) gets practical about agent permissions.
The summit brings together a curated room of 150–200 CISOs, CTOs and enterprise architects, with speakers from organisations including Microsoft, Accenture, KPMG and Infosys. Review the full agenda or secure your delegate pass.
Frequently asked questions
What is zero trust AI security?
Zero trust AI security is the application of never trust, always verify to every part of an AI system. Each request to a model, tool or dataset is authenticated, authorised and logged individually, rather than trusted because it comes from inside the network.
How is zero trust for AI different from traditional zero trust?
The principles are the same, but AI adds new things to verify: model provenance, retrieved content, agent actions and natural-language inputs that can carry instructions. Controls therefore extend to AI gateways, permission-aware retrieval and scoped tool access for agents.
Does zero trust stop prompt injection?
Not on its own. Zero trust cannot stop a model from reading malicious text, but it limits what a manipulated model or agent can reach, which sharply reduces the impact of a successful injection.
Where can I learn about zero trust AI architecture in Dubai?
Enterprise Private AI UAE 2027 in Dubai on 17–18 March 2027 dedicates Day 2 to security, agents and governance. Sessions include a technical keynote on securing LLMs across hybrid environments and a deep-dive lab on AI identity.