The core enterprise AI security best practices are to know every AI system you run, enforce identity and least privilege on every model and agent, keep data access permission-aware, validate what models produce, and monitor AI activity at runtime. Applied together, these controls let organisations scale AI adoption without losing control of sensitive data or business processes.
This article sets out ten practical controls, grouped into governance, protection and runtime, and suggests who should own each one. It is written for CISOs, CTOs and platform leaders who need a programme, not a product list.
Why AI security needs its own playbook
Many existing security controls still apply to AI: identity, encryption, network segmentation and vulnerability management do not stop being relevant. But AI systems behave differently from conventional applications in ways that create genuinely new risk.
- Inputs can carry instructions. Prompt injection, listed as LLM01 in the OWASP Top 10 for LLM Applications 2025, exploits the fact that models cannot reliably separate commands from data.
- Outputs are non-deterministic. The same prompt can produce different answers, so testing and assurance work differently.
- Data spreads into new stores. Prompts, logs, caches, embeddings and fine-tuning sets all hold copies of sensitive information.
- Agents act on behalf of people. Once AI can call tools and APIs, every permission becomes a potential blast radius.
The practical consequence is that AI security cannot be bolted on at the end of a project. The controls below work best when they are built into the platform that teams use to ship AI, so that the secure path is also the easiest path for developers and business users.
Govern: best practices 1 to 3
1. Maintain a living AI inventory
You cannot secure what you cannot see. Record every model, endpoint, agent, vector store, fine-tuned variant and AI feature embedded in SaaS tools, along with its owner, data sources and the business process it supports. Include shadow usage discovered through network and expense data.
2. Tier use cases by risk
Classify each use case by the sensitivity of its data and the impact of its actions. An internal drafting assistant and an agent that can change customer records should not carry the same controls. Risk tiers let you move quickly on low-risk work and concentrate effort where it matters.
3. Publish a clear acceptable use policy
Tell employees which AI tools are approved, which data classes may be used with which tools, and how to request something new. A short, specific policy is more effective than a long, abstract one, and it reduces shadow AI by offering a sanctioned path. Review it at least as often as your approved tool list changes.
Protect: best practices 4 to 7
4. Put identity on every AI call
Replace shared API keys with short-lived, identity-based credentials, and make sure every request to a model can be traced to a user, application or agent. This is the foundation of zero trust AI security.
5. Route model traffic through an AI gateway
A central gateway gives you one place to enforce model allow-lists, apply input and output filtering, manage budgets and capture audit logs, whether models are hosted APIs, self-hosted on GPUs or deployed at the edge.
6. Keep data access permission-aware
Retrieval systems should only return content the requesting user is already entitled to see. Classify data before indexing it, avoid all-seeing service accounts and apply the same retention rules to embeddings and logs as to the source data.
7. Secure the model supply chain
Source models and libraries from approved registries, verify artefact integrity, scan dependencies, and document which base model, data and configuration produced each deployed version.
Constrain and monitor: best practices 8 to 10
8. Scope agent permissions tightly
Give agents their own identities, task-specific tool allow-lists and time-bound credentials. Require human approval for irreversible or high-value actions, and limit outbound channels so a manipulated agent cannot quietly send data elsewhere.
9. Validate outputs before they act
Treat model output as untrusted input to the next system. Enforce schemas, constrain parameters and never pass generated text straight into code execution, queries or shell commands. Our guide on how to prevent prompt injection across the enterprise explains why this layer matters so much.
10. Monitor at runtime and test continuously
Log prompts, retrieved content, outputs and tool calls with appropriate redaction, alert on anomalies, and run regular red-team exercises against real workflows. Good AI observability turns written policy into evidence that controls are working.
Who owns each enterprise AI security control
AI security fails most often at the seams between teams. The table below is a starting point for assigning ownership; the right split will depend on your operating model.
| Practice | Primary owner | Key partners |
|---|---|---|
| AI inventory and risk tiers | CISO or AI governance lead | Business owners, procurement, enterprise architecture |
| Acceptable use policy | CISO with legal and compliance | HR, internal communications |
| Identity and AI gateway | Platform engineering | Identity and access management, security architecture |
| Permission-aware data access | Data platform team | Data owners, privacy office |
| Model supply chain | ML engineering | Application security |
| Agent permissions and approvals | Product or use-case owner | Security architecture, platform engineering |
| Runtime monitoring and red-teaming | Security operations | ML engineering, AI governance lead |
In regulated sectors and in jurisdictions such as the UAE, where Federal Decree-Law No. 45 of 2021 and the separate DIFC and ADGM regimes apply, involve legal and compliance early and confirm obligations with them rather than relying on technical controls alone.
If you are starting from scratch, sequence the work. In the first few months, build the inventory, publish the policy and stand up a gateway with identity on every call. Next, fix data access for retrieval and scope any agents already in production. Then invest in monitoring and red-teaming so you can prove the controls hold as usage grows.
For the governance side of this picture, see AI governance at runtime.
Benchmark your AI security programme at Enterprise Private AI UAE 2027
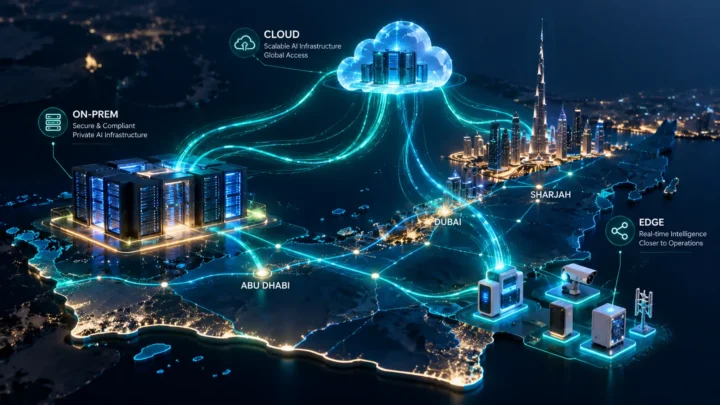
Day 2 of Enterprise Private AI UAE 2027, held in Dubai on 17–18 March 2027, is dedicated to security, agents and governance. The Technical Keynote Securing LLMs Across Hybrid Enterprise Environments (Day 2, 10:00) covers controls across cloud, on-prem and edge, and the Governance Session AI Governance at Runtime: Moving Beyond Policies and Checklists (Day 2, 16:00) focuses on turning policy into enforcement.
Compare approaches with a curated room of CISOs and technology leaders, with speakers from organisations including Accenture, KPMG, Infosys and Microsoft. See the agenda or reserve your pass.
Frequently asked questions
What are the most important enterprise AI security best practices?
The most important practices are maintaining an AI inventory, enforcing identity and least privilege on every model and agent, applying permission-aware data access, validating outputs, and monitoring AI activity at runtime. Together they cover the main risks without blocking adoption.
Who should own AI security in an enterprise?
The CISO typically owns AI security policy and controls, but delivery is shared with platform engineering, data teams and the business owners of each AI use case. Clear ownership for each control matters more than a single owner for everything.
How is AI security different from application security?
AI systems accept natural language that can carry instructions, generate non-deterministic outputs and often act on behalf of users. That adds risks such as prompt injection, data leakage through embeddings and over-privileged agents, which traditional application security tools do not fully address.
Is there an event in Dubai focused on enterprise AI security?
Yes. Enterprise Private AI UAE 2027 in Dubai on 17–18 March 2027 dedicates Day 2 to security, agents and governance, including keynotes on securing LLMs and runtime AI governance.