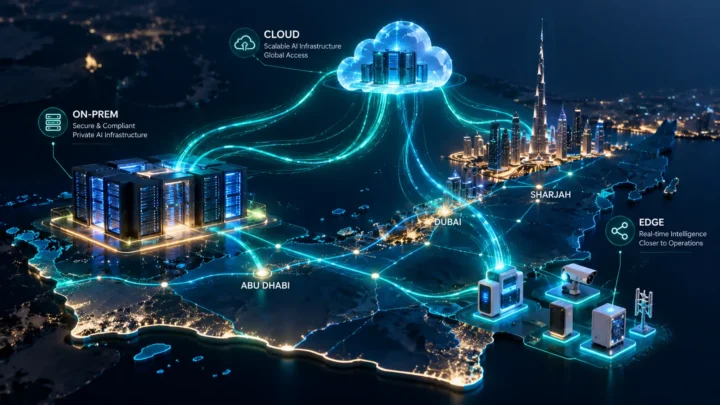
Private AI is the practice of running AI models, and the data and tooling around them, in an environment your organisation controls, so that prompts, documents, embeddings and outputs are not exposed to parties you have not approved. It is defined by control rather than location: it can sit in a private cloud, an on-premises data centre, a sovereign cloud region or at the edge. For UAE enterprises, it is chiefly a way to use large language models (LLMs) on sensitive data while meeting residency, security and governance expectations.
What does private AI actually mean?
The term is used loosely, and vendors stretch it to fit whatever they sell. A more useful definition starts with four questions about who holds the keys. If your organisation cannot answer all four with confidence, the deployment is only partly private.
The four controls
- Data control: you decide where prompts, retrieved documents, logs and embeddings (numerical representations of text used for search) are stored, who can read them, and how long they persist.
- Model control: you choose which model version runs, you can pin it, and nobody changes it underneath you or uses your data to train it without agreement.
- Infrastructure control: you know which facilities, jurisdictions and operators host the compute, and you can enforce network boundaries around it.
- Operational control: you hold the monitoring, access management, audit trails and incident response for the whole system.
Private AI is therefore a spectrum. A model hosted in a dedicated environment with strict contractual terms is more private than a shared public endpoint, and a model running in your own facility, with your own keys and logging, is more private again.
What private AI is not
Three common misreadings cause poor decisions.
- It is not the same as on-premises. On-premises hardware is one way to achieve control, but a badly governed on-premises cluster can leak data as easily as any other system.
- It is not the same as open-source models. Open-weight models make self-hosting possible, yet a proprietary model deployed in a controlled environment can also qualify. The licence and the operating model matter more than the label.
- It is not isolation from everything. Most useful private AI systems still connect to internal applications, identity providers and sometimes external services. The question is whether each connection is deliberate and governed.
Where can private AI run?
There are four common deployment patterns. They differ in control, effort and flexibility, and most large organisations end up using more than one.
| Pattern | Control level | Typical strength | Main trade-off |
|---|---|---|---|
| Public API with contractual protections | Lower | Fast to start, access to the largest models | Data leaves your boundary; less visibility of the runtime |
| Private or dedicated cloud environment | Medium to high | Elastic capacity with isolated tenancy | Depends on provider controls and region choices |
| On-premises or colocation | Highest | Full ownership of data path and hardware | Capital cost, GPU supply and skills burden |
| Edge | High for local data | Low latency; data stays at the site | Smaller models and harder fleet management |
For a closer look at the first decision in that table, see our guide to private AI versus public cloud LLMs.
Why are UAE and GCC enterprises paying attention?
Several pressures converge in the region. Banks, insurers, healthcare providers, energy operators and government entities hold data that carries strict handling expectations. National and sector-specific rules on data protection and residency shape where information may be processed, and boards increasingly ask where their prompts and documents actually go.
There is also a strategic dimension. Sovereign AI, meaning national or organisational capacity to build and run AI without dependence on a single foreign provider, is a stated priority across the Gulf. Enterprises feel this as a procurement question: which parts of the AI stack must be owned, and which can be rented?
Private AI is not a legal exemption, and it does not by itself make a system compliant. Requirements vary by sector, data type and use case, so confirm specifics with legal and compliance teams. Our article on private AI and UAE data law explains what to ask them.
How do you decide whether a workload needs private AI?
Not every workload justifies the cost of full control. A drafting assistant working on public marketing copy has different needs from a model summarising customer financial records. Apply five tests to each use case and let the answers set the level of privacy.
- Data sensitivity: does the workload touch personal, financial, health, commercial or government-classified information?
- Residency and jurisdiction: must the data, including logs and embeddings, stay within the UAE or a defined jurisdiction?
- Auditability: do you need to prove, after the event, what the model saw and produced?
- Performance profile: does it need predictable latency, offline operation or proximity to a site or device?
- Economics: is usage steady and high enough that owned or reserved capacity could cost less than per-token pricing, once staff and operations are counted?
A workload that fails the first three tests is a strong candidate for a controlled environment. One that fails only the fifth is a cost question, and our comparison of self-hosted LLM and API cost covers how to model it.
These trade-offs are the working focus of Enterprise Private AI UAE 2027, the technical summit taking place in Dubai on 17–18 March 2027, where practitioners compare how they have drawn these lines in production.
What does a private AI stack include?
A model is only one layer. Control depends on the whole chain, and gaps in any layer can undo the privacy of the rest.
- Compute and hosting: GPUs or accelerators in an environment you can place and inspect.
- Models: one or several, often a mix of larger general models and smaller specialised ones, served through a controlled inference layer.
- Data layer: document stores, vector databases and retrieval pipelines that respect existing access rights.
- Security layer: identity, encryption, network segmentation and protection against prompt injection, where hostile text tries to override the model’s instructions.
- Governance and observability: usage logging, evaluation, cost tracking and policy enforcement at runtime.
Deciding which of these layers to build, buy or rent is a strategic choice in its own right. We examine it in what enterprises should own versus rent in the sovereign AI stack.
What are the common mistakes?
Treating privacy as a hosting decision only
Teams move a model into a private environment and forget the surrounding data flows. Logs, caches, evaluation datasets and embeddings often hold copies of sensitive content, and they frequently sit outside the controls applied to the model itself.
Buying hardware before defining workloads
GPU capacity is expensive and quickly specialised. Organisations that purchase first and find use cases later often end up with the wrong capacity profile. Start with two or three well-understood workloads and measure real demand.
Ignoring the operating model
Running inference reliably needs skills in platform engineering, security and model evaluation. If no team owns patching, capacity planning and incident response, control exists on paper only.
Assuming one pattern fits everything
A single public endpoint for all workloads is too loose for sensitive data, and a single on-premises cluster for all workloads is too rigid for experimentation. A hybrid estate with clear routing rules is usually the more realistic answer.
Next steps for your team
If your organisation is defining its position on private AI, a short, structured exercise will do more than another vendor briefing.
- List the AI use cases in production or planned, and classify the data each one touches.
- Score each use case against the five tests above and assign a target control level.
- Map where prompts, logs, caches and embeddings are stored today, and close the gaps you find.
- Name a single accountable owner for the AI platform, with security and compliance involved from the start.
- Pilot one sensitive workload in a controlled environment and measure latency, quality and total cost against your current approach.
To test your conclusions against peers, review the summit programme and agenda for the Dubai event in March 2027, and bring your classification results with you. They make the discussions far more concrete.
Frequently asked questions
What is private AI in simple terms?
Private AI is AI that runs in an environment your organisation controls, so your data, prompts and outputs stay within boundaries you set. It can be hosted in a private cloud, on-premises, in a sovereign cloud region or at the edge. What matters is control over data, models, infrastructure and operations.
Is private AI the same as on-premises AI?
No. On-premises is one way to deliver private AI, but a dedicated private cloud or a sovereign cloud region can also qualify. The test is whether you control the data path, the model version, the hosting location and the audit trail.
Does private AI make an enterprise compliant with UAE data rules?
No, private AI helps with compliance but does not guarantee it. Obligations depend on the sector, the type of data and the use case. Confirm specific requirements with your legal and compliance teams before deciding on an architecture.
Do all enterprise AI workloads need to be private?
No. Low-sensitivity workloads, such as drafting public content, can often use public services under suitable contract terms. Reserve the higher-control environments for workloads involving sensitive data, strict residency needs or strong audit requirements.
What is the first step towards private AI?
Start by inventorying your AI use cases and classifying the data each one handles. That shows which workloads need stronger control and which do not. You can then pilot one sensitive workload in a controlled environment and compare results.